

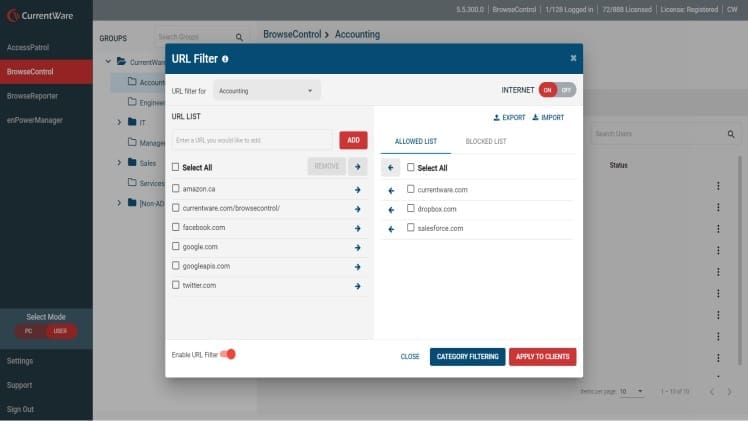
When it comes to network security, firewalls play an important role. They protect against malicious threats, such as malware and viruses, as well as unauthorized access. But not all firewalls are created equal. Some offer more robust protection than others, including the ability to filter web content requests, such as URLs and domain names. In this article, we’ll compare the different types of firewalls to determine which offers the best protection when it comes to web content filtering.
Comparing Firewall Web Content Filtering
When it comes to web content filtering, there are two main types of firewalls: application-level firewalls and network-level firewalls. Application-level firewalls are designed to filter traffic based on the applications being used. For example, they can be set to block certain applications or websites. Network-level firewalls, on the other hand, are designed to filter traffic based on the network connection. They can be set to block certain IP addresses or networks.
When it comes to web content filtering, application-level firewalls are generally considered to be more effective than network-level firewalls. This is because application-level firewalls can more easily block malicious requests, such as those from malicious websites. Network-level firewalls, on the other hand, are better suited for filtering web traffic based on IP addresses and networks.
Evaluating URL and Domain Name Filtering
When it comes to filtering web content requests, such as URLs and domain names, application-level firewalls are the best choice. This is because they can more easily detect malicious requests and block them. Network-level firewalls, on the other hand, are better suited for filtering web traffic based on IP addresses and networks.
In addition to filtering requests based on URLs and domain names, application-level firewalls can also be used to block certain applications and websites. This is useful for preventing users from accessing certain types of content, such as malicious websites or sites that contain inappropriate content.
Overall, application-level firewalls are the best choice when it comes to filtering web content requests, such as URLs and domain names. They offer more robust protection than network-level firewalls, and can be used to block malicious requests as well as certain applications and websites.
When it comes to web content filtering, application-level firewalls are the best choice. They offer more robust protection than network-level firewalls, and can be